🏢
Multi-Org Management
Add and switch between multiple Jamf Pro (Jamf Cloud) instances from a single app, each with its own API credentials.
📜
Playbooks
Declare Smart Groups, Policies, Scripts, Configuration Profiles and more as YAML — plan, apply, and schedule recurring runs. Import shared playbooks from the community repo.
🧠
AI Assistant
An in-app chat assistant built on Apple's Foundation Models framework — ask questions about your Jamf environment. Requires Apple Intelligence enabled on your Mac.
🔌
MCP Server
Turn Jarl into a local MCP server so any MCP-compatible AI tool can query and manage your Jamf environment. Read tools on by default; write tools are opt-in.
🕸️
Relationship Map
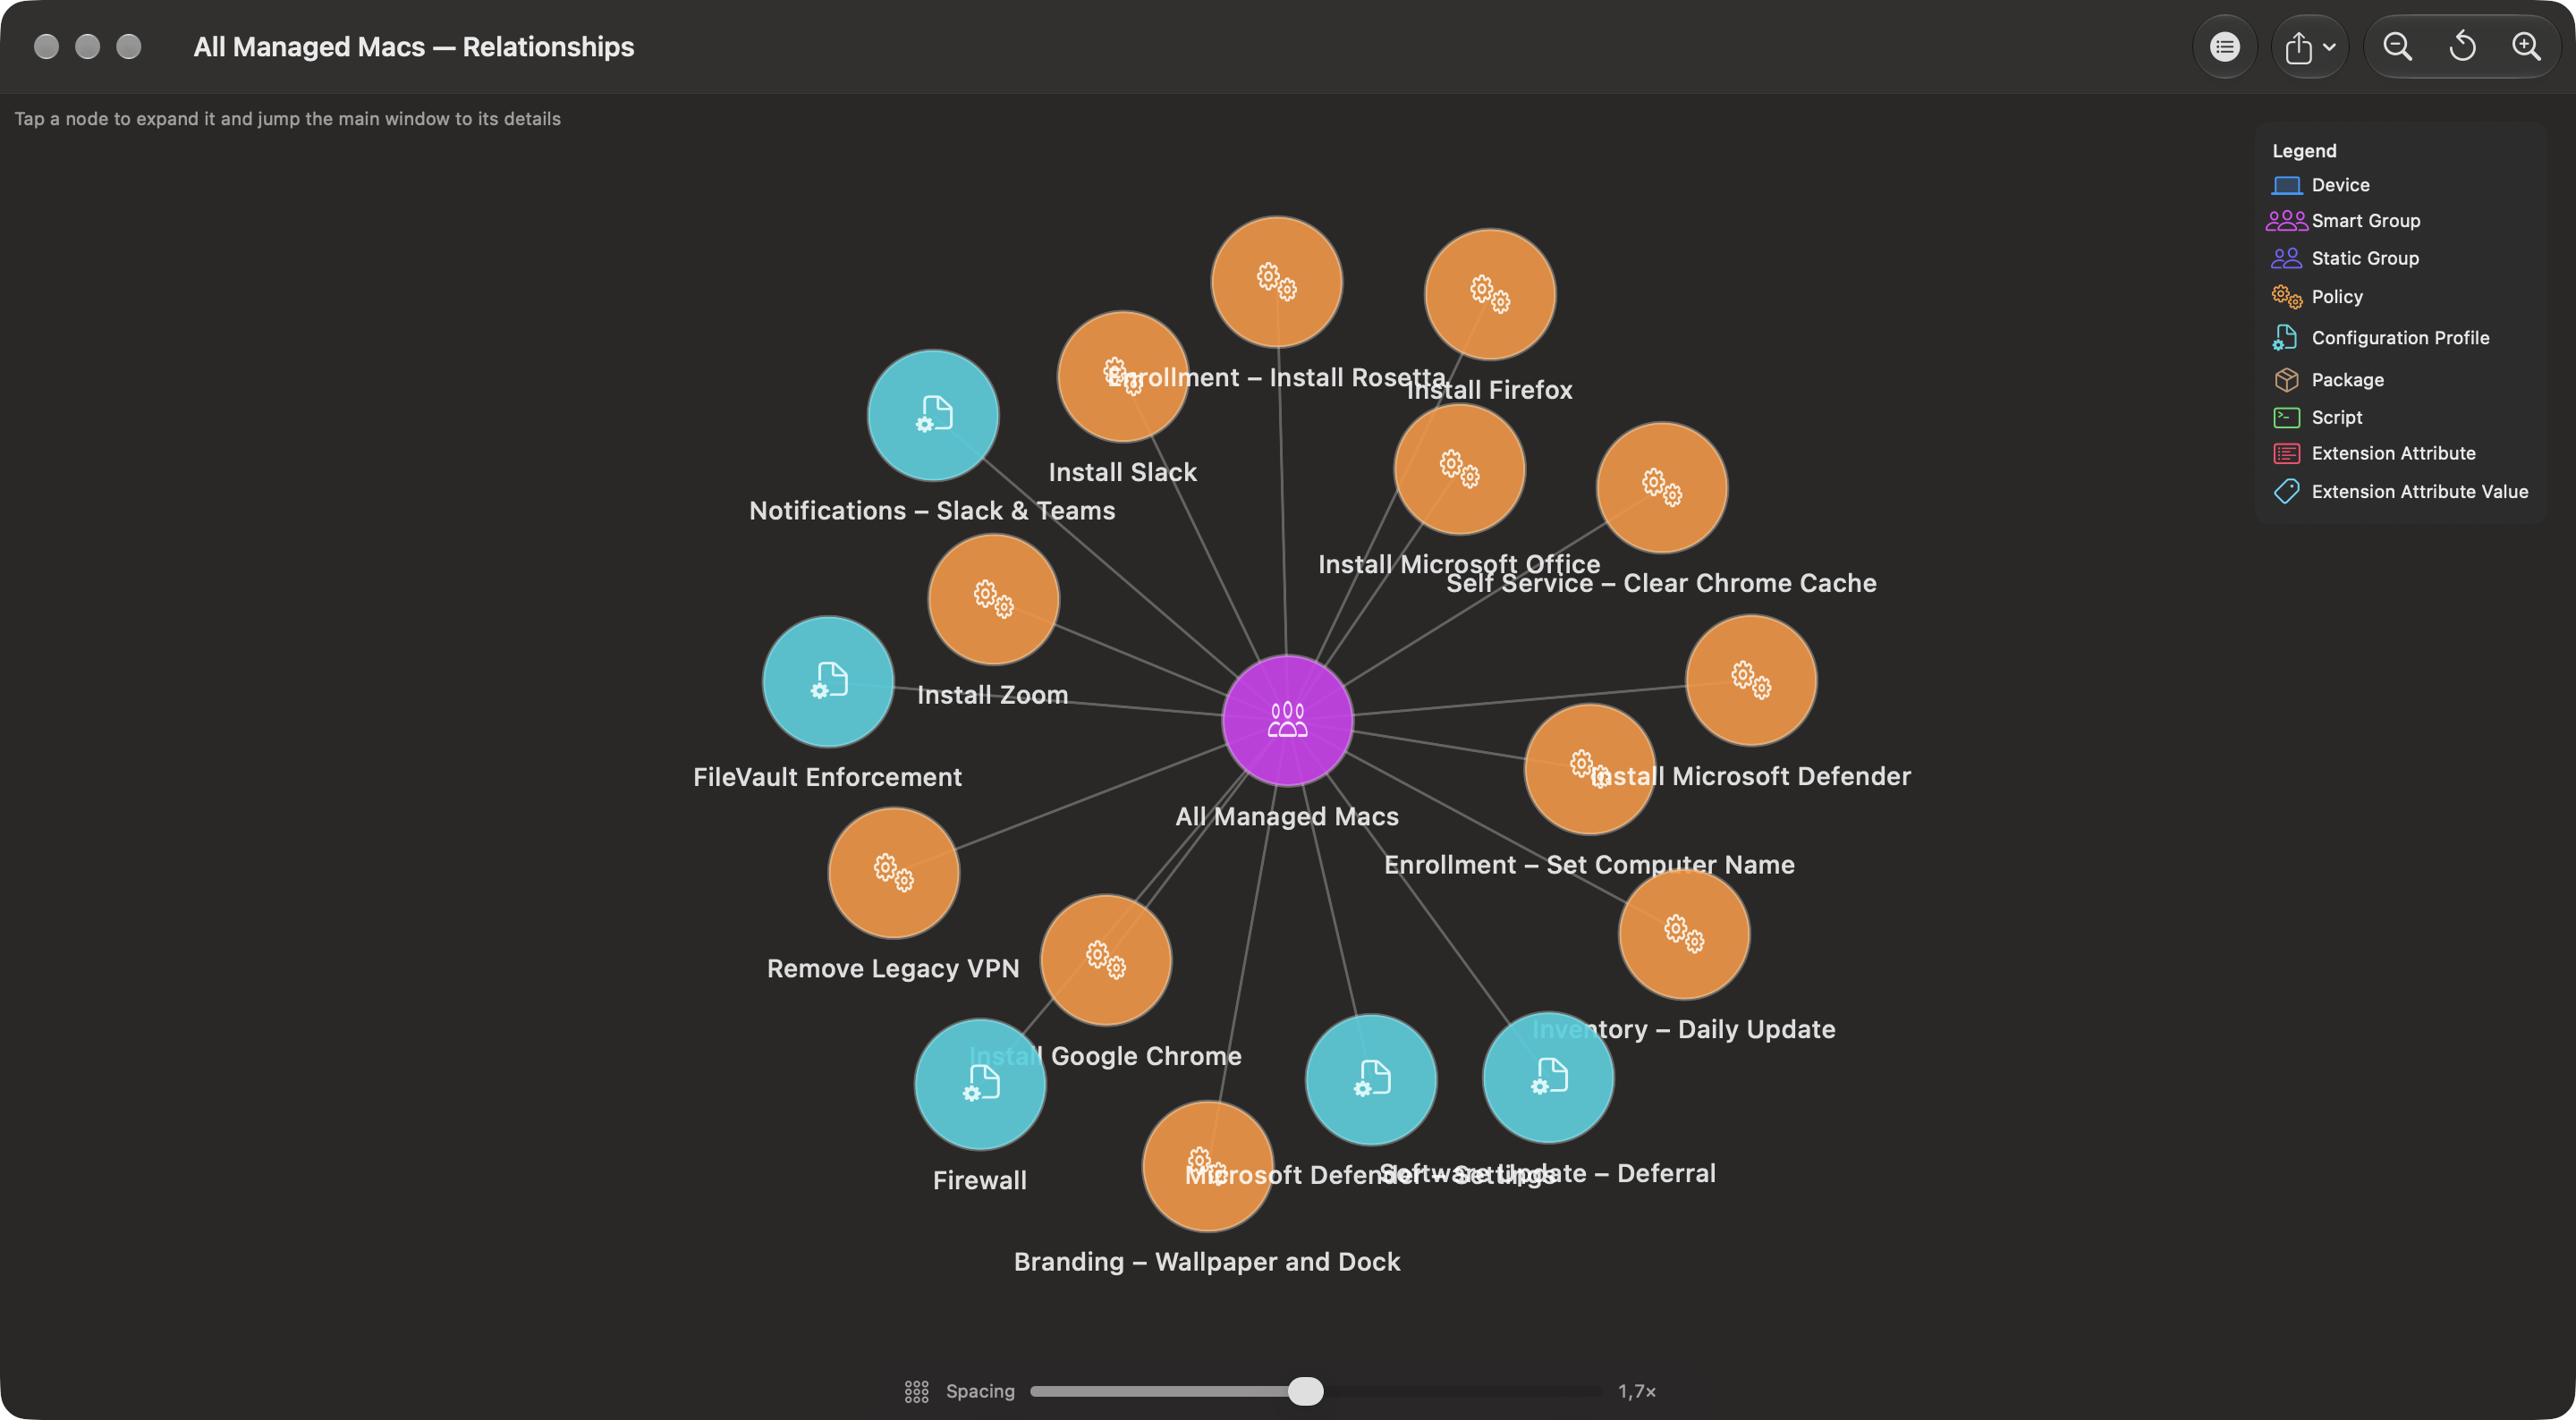
A visual graph of how devices, groups, policies, profiles, scripts and extension attributes depend on each other — see the blast radius before you change anything.
💾
Backups
Export Smart Groups, Static Groups, Policies, Scripts, Configuration Profiles, Packages and Extension Attributes to local JSON, on demand or on a schedule.
🗄️
Gimle Backups
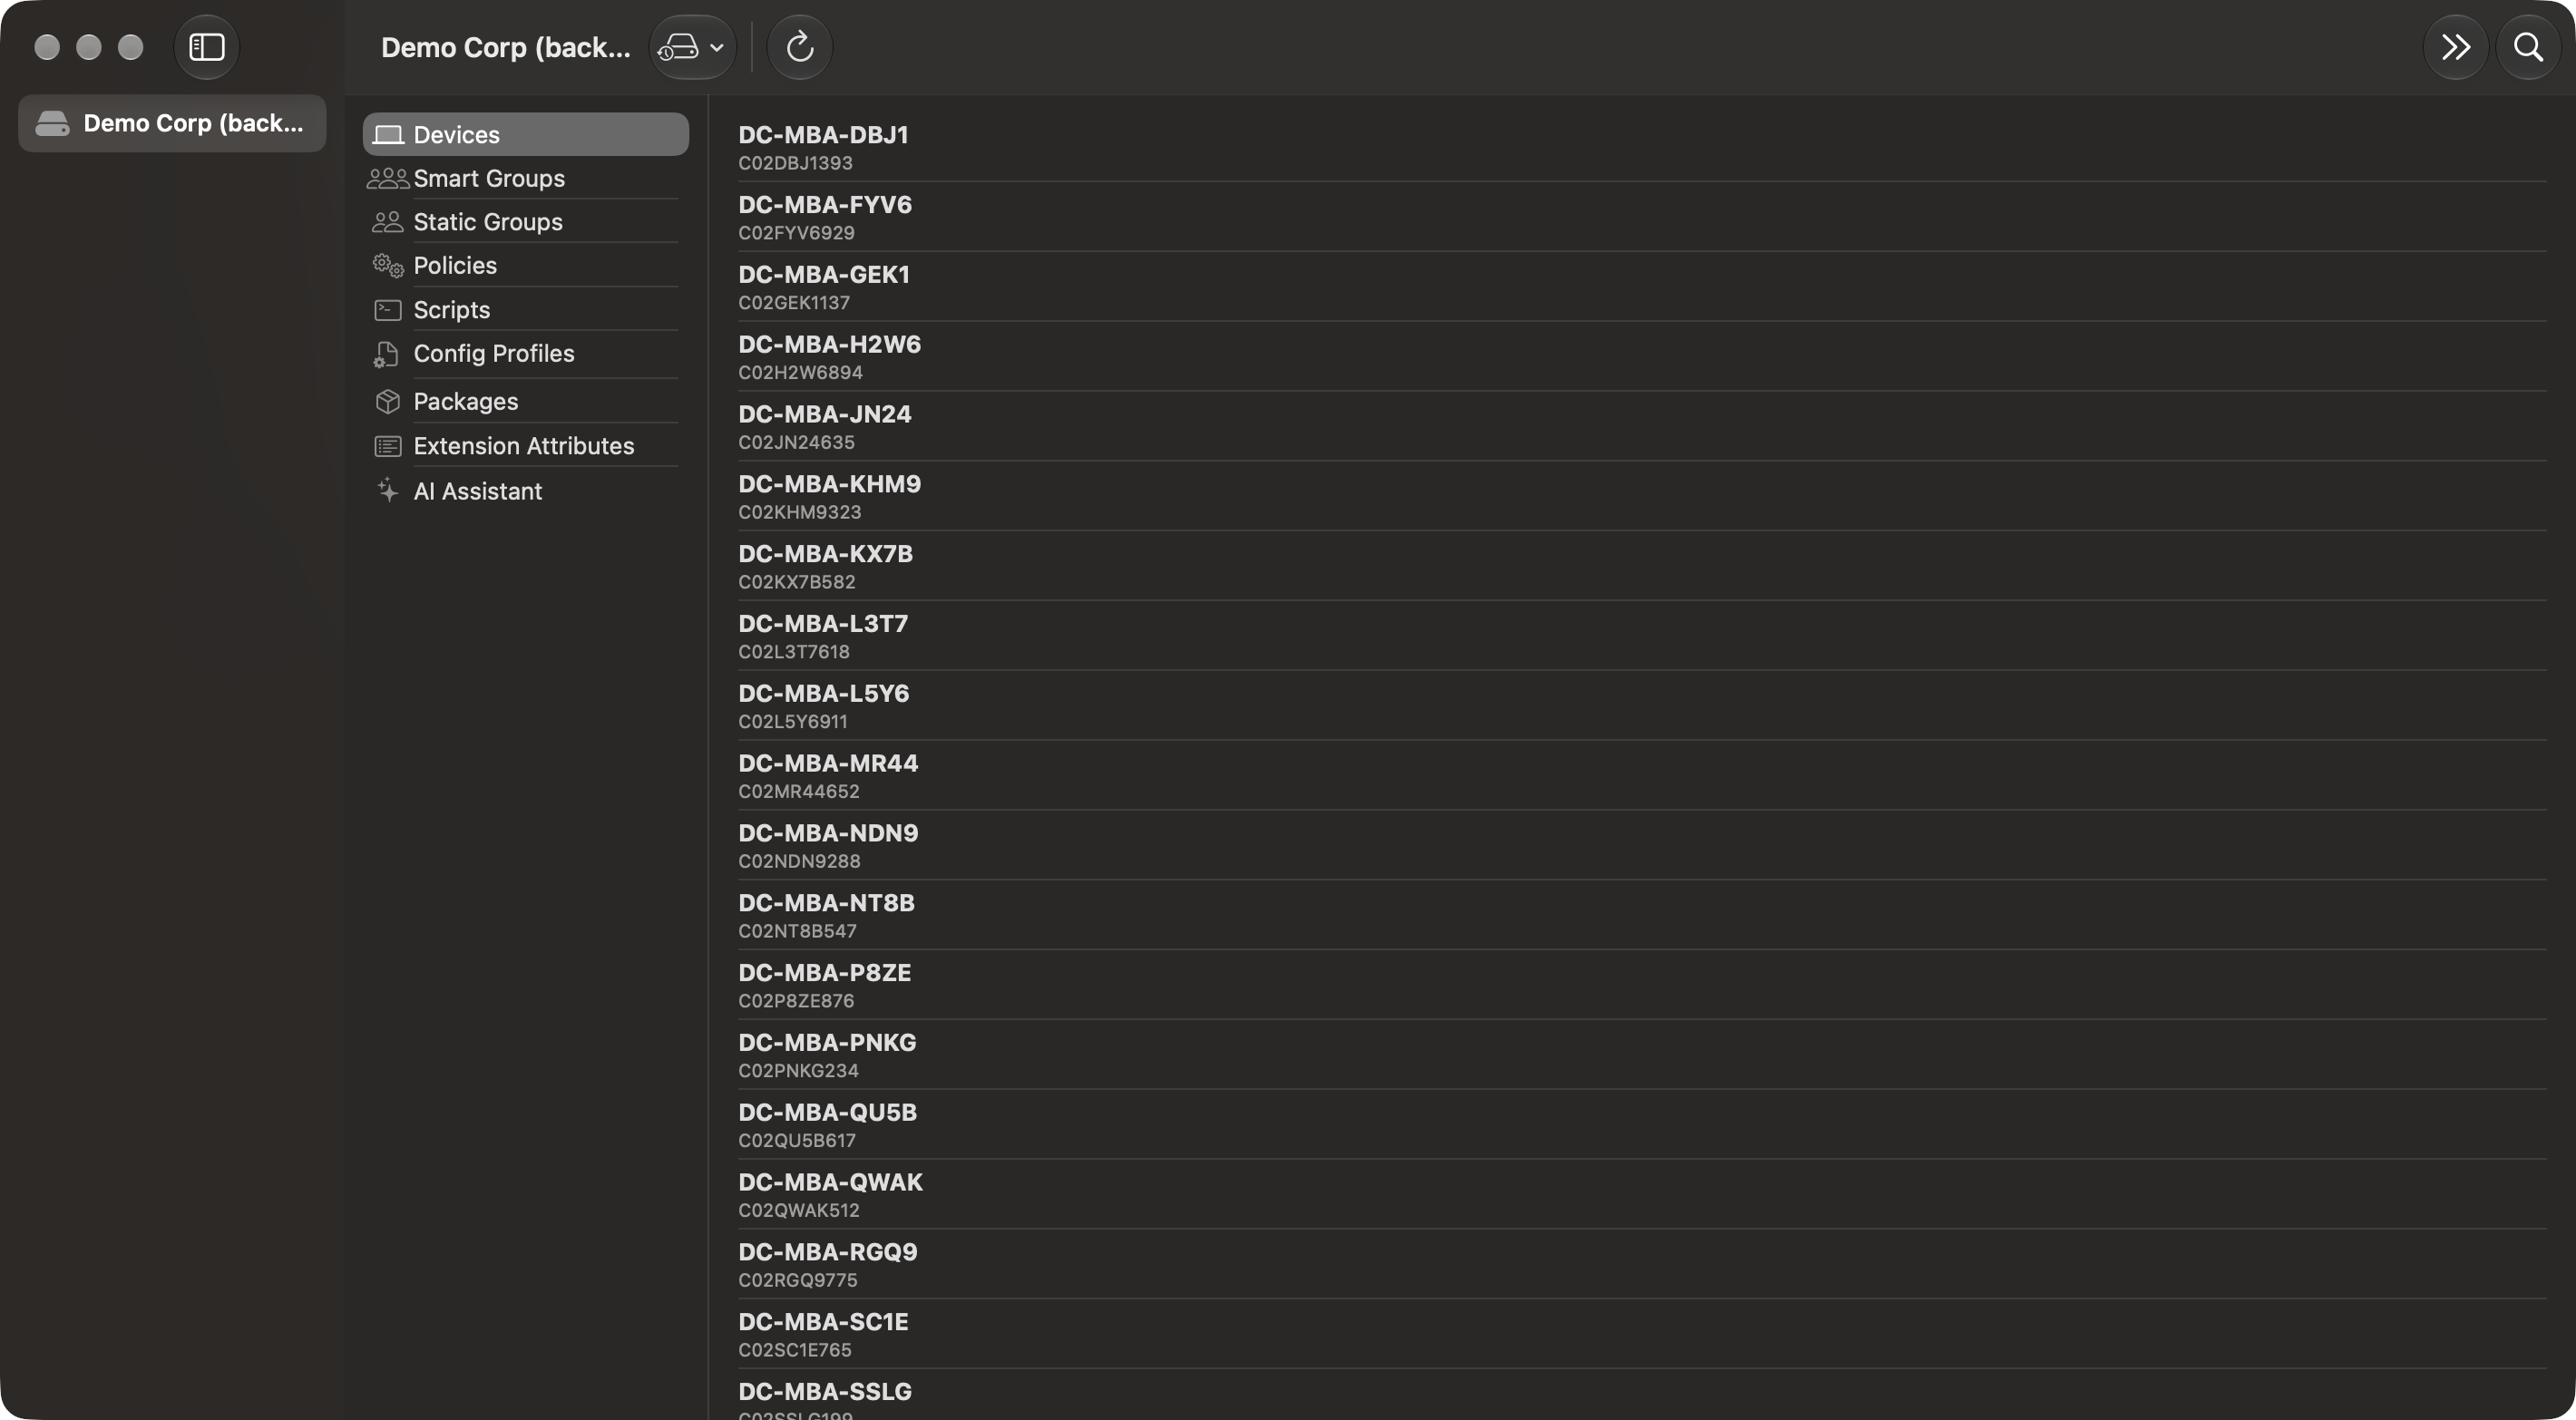
Open a backup made by Gimle, the read-only Jamf Pro backup tool, as an offline organization. Browse devices, groups, policies, profiles, scripts and the relationship map with no connection to Jamf, and step back through older backups like Time Machine. Read-only by design.
🛡️
Managed Deployment
Push organizations to your team's Macs with MDM. The Jamf API credentials arrive in a configuration profile, encrypted with your organisation key, and users can neither see nor change them.
🔁
Copy Between Orgs
Copy a policy, group, script or profile from one Jamf Pro tenant straight into another, with org-specific fields like scope handled per resource type.
🔐
Secure by Design
OAuth 2.0 client credentials, no Jamf user accounts or SSO. Secrets live in the macOS Keychain, gated behind Touch ID / Face ID before they're revealed.
💻
Device Inventory
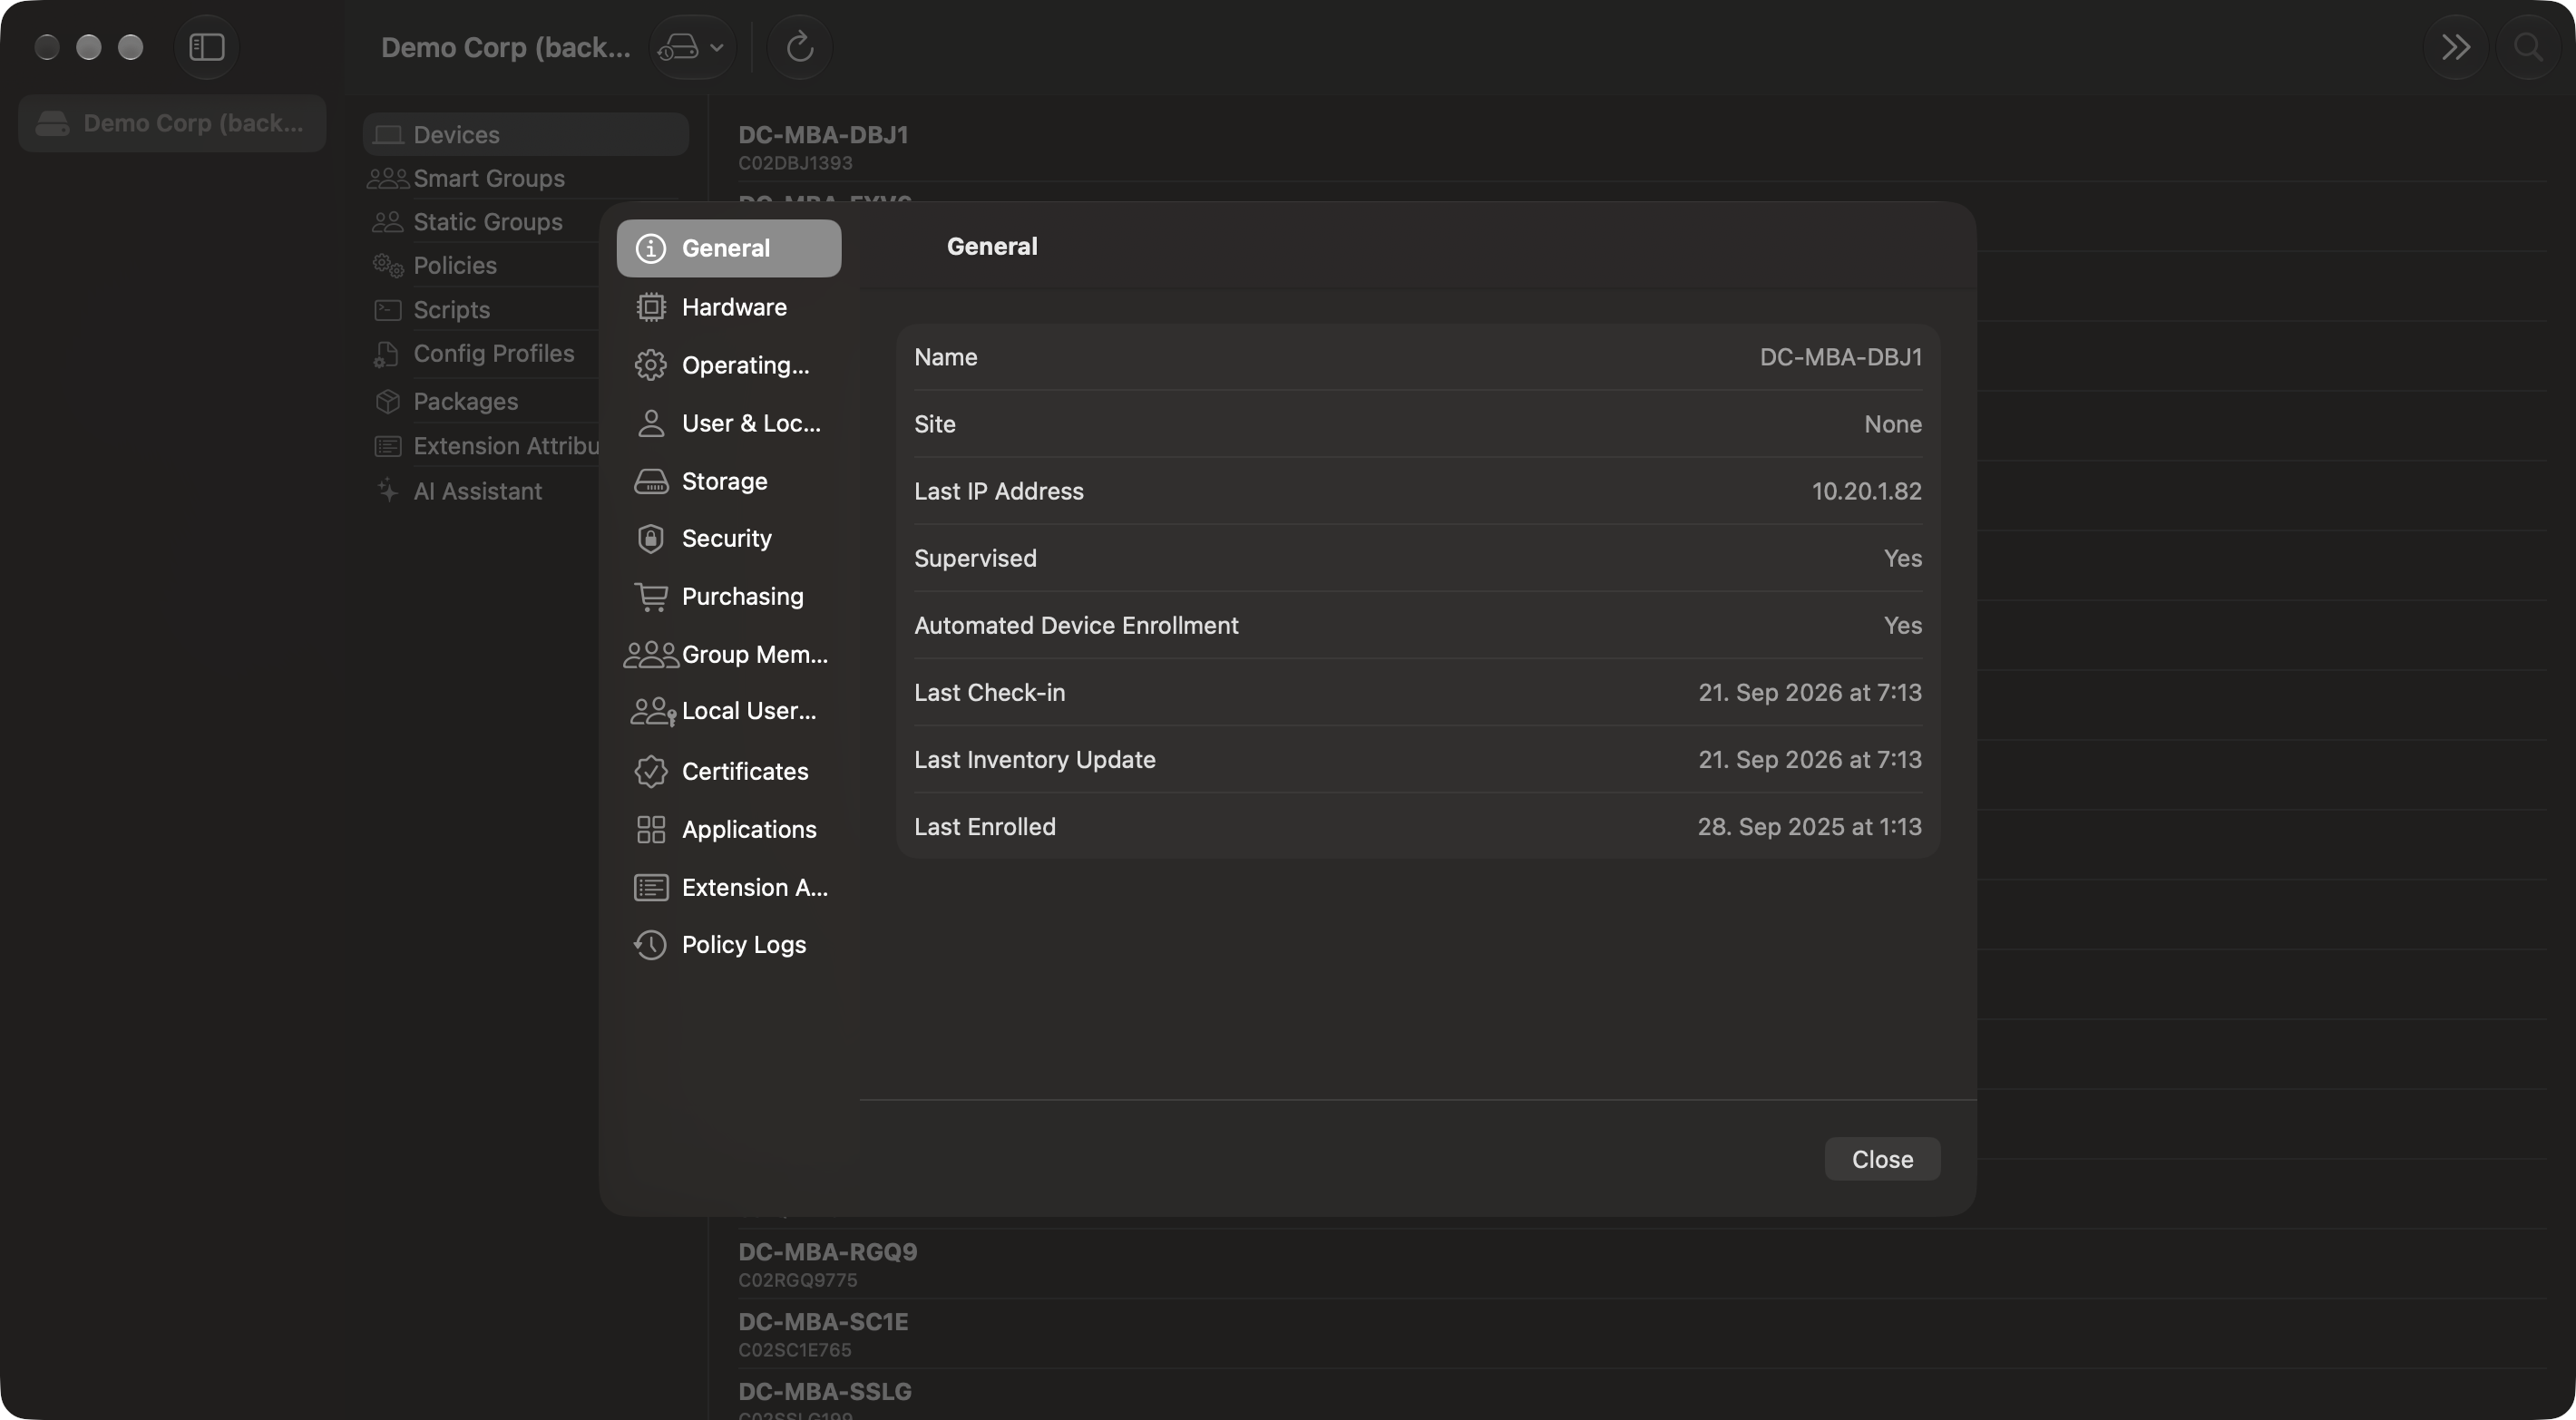
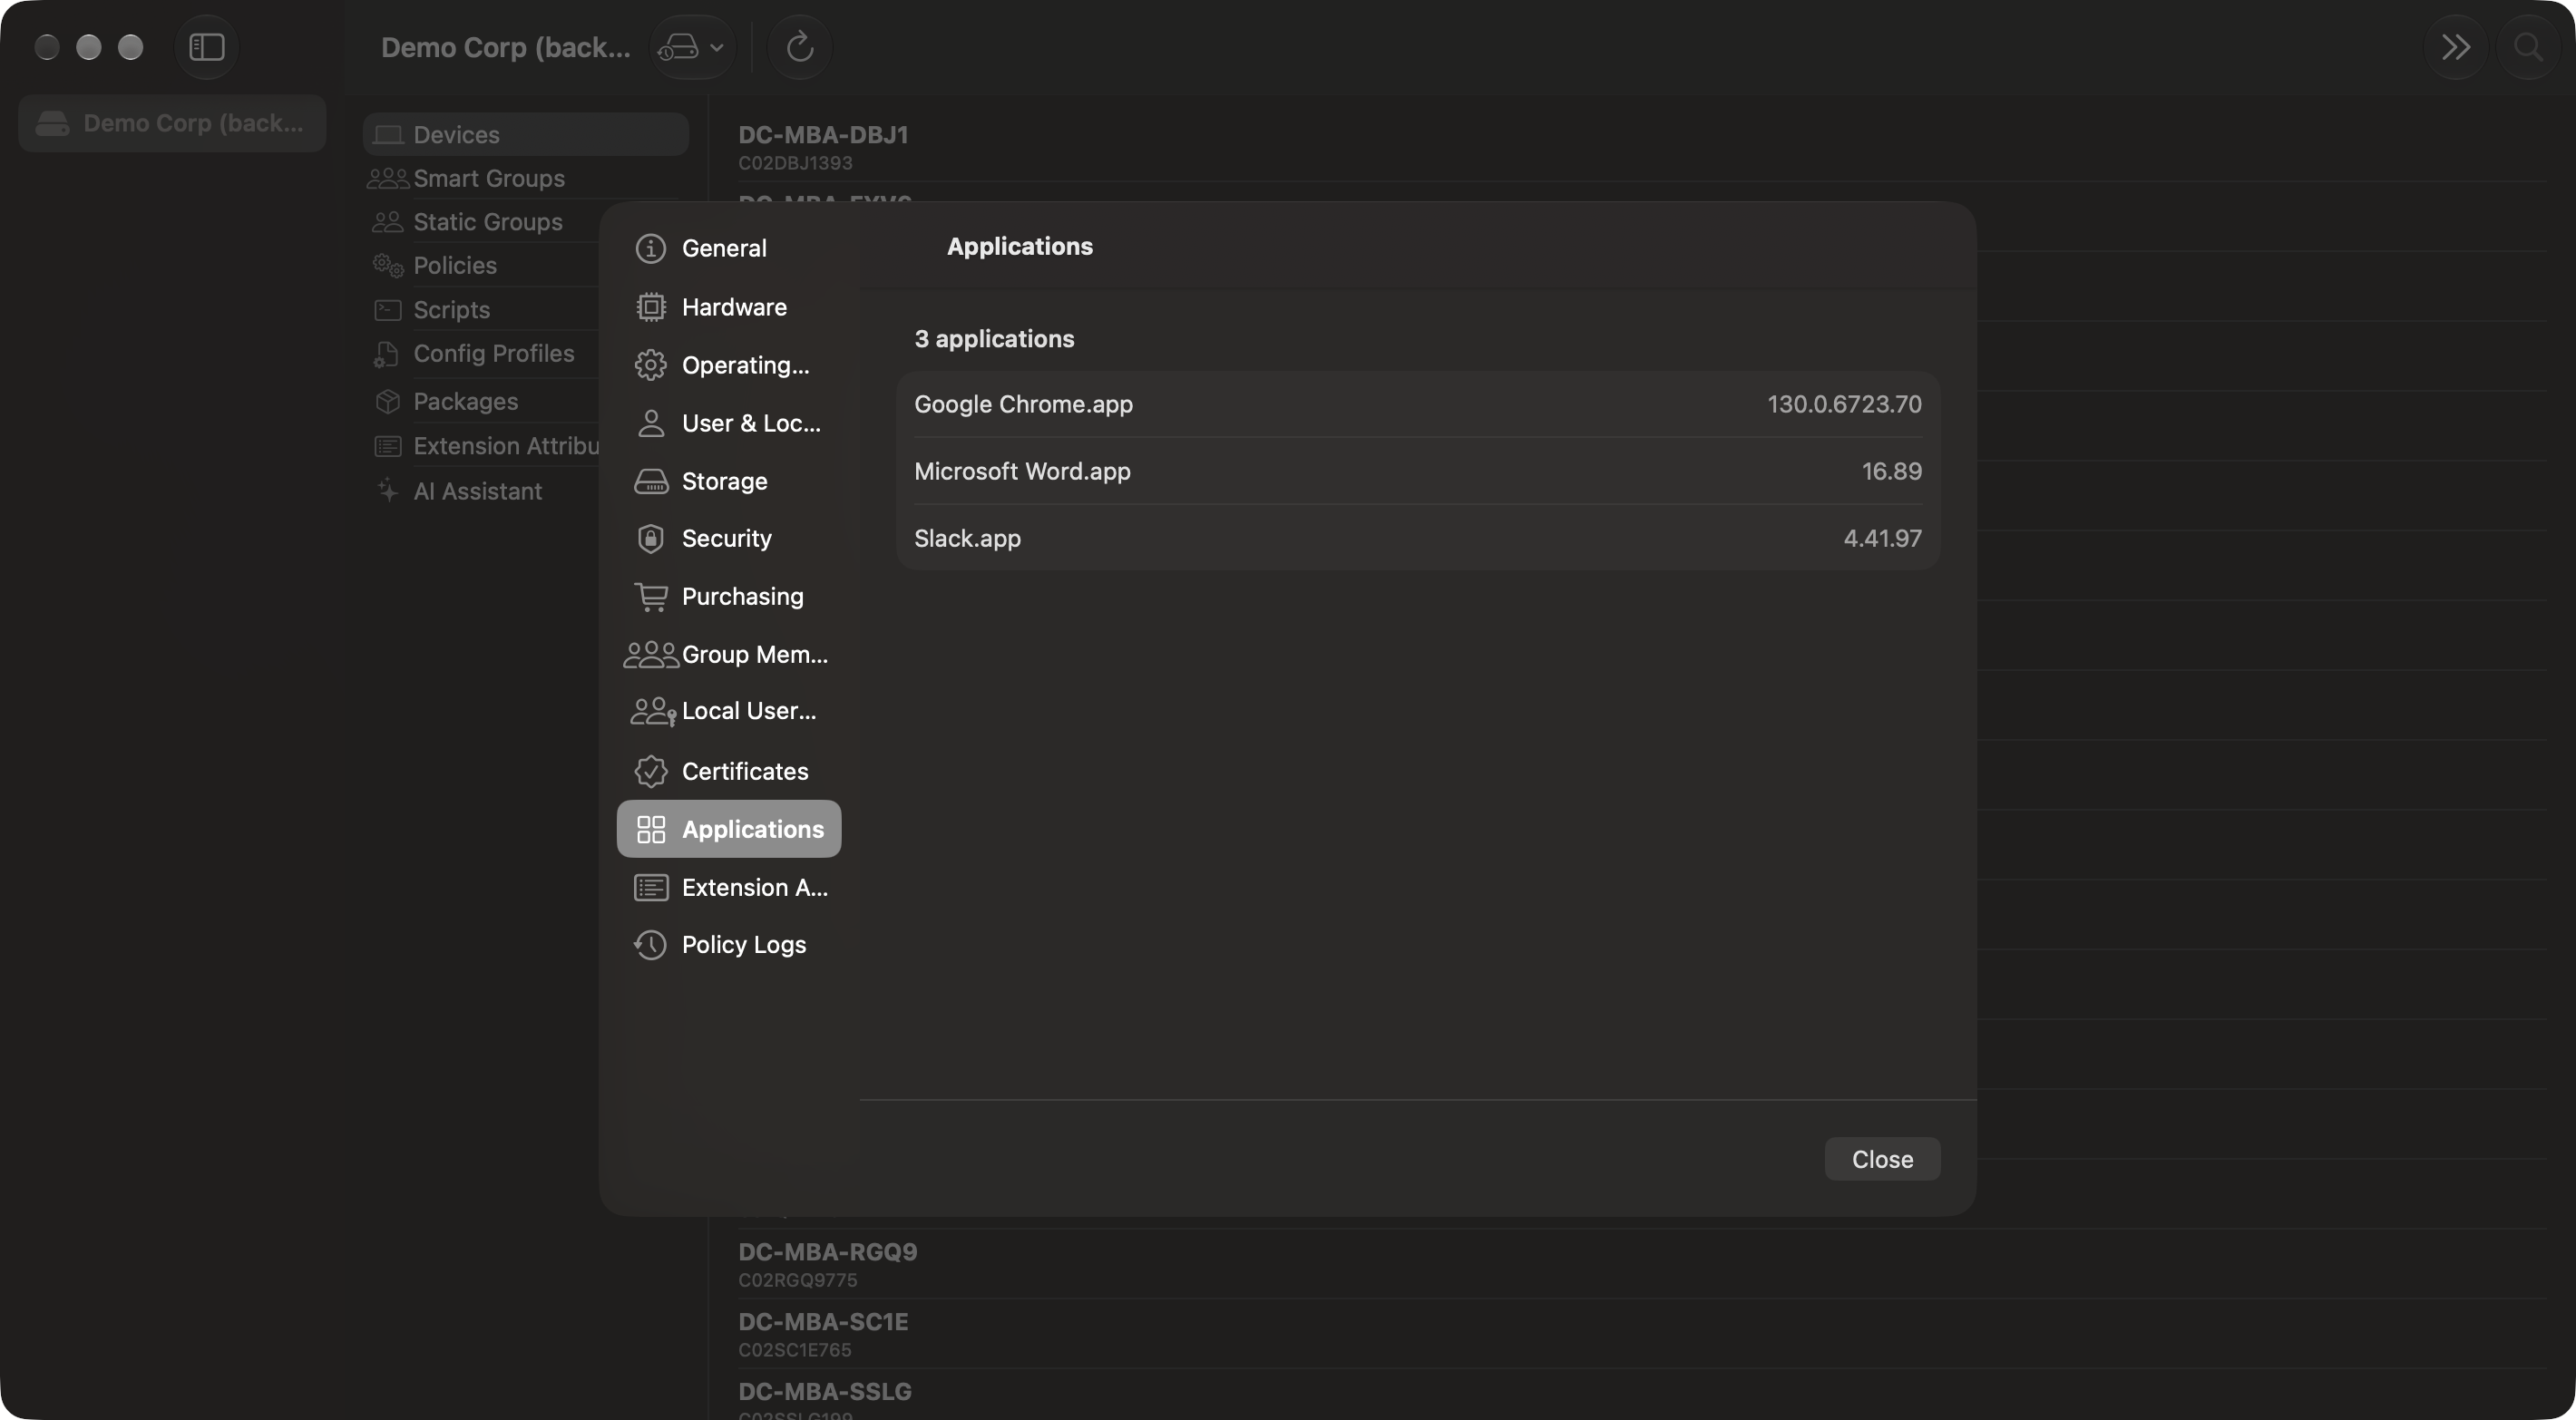
Browse device inventory across every connected org, with rename and asset-tag editing built in, cached locally for instant reopen.
📋
Policies & Smart Groups
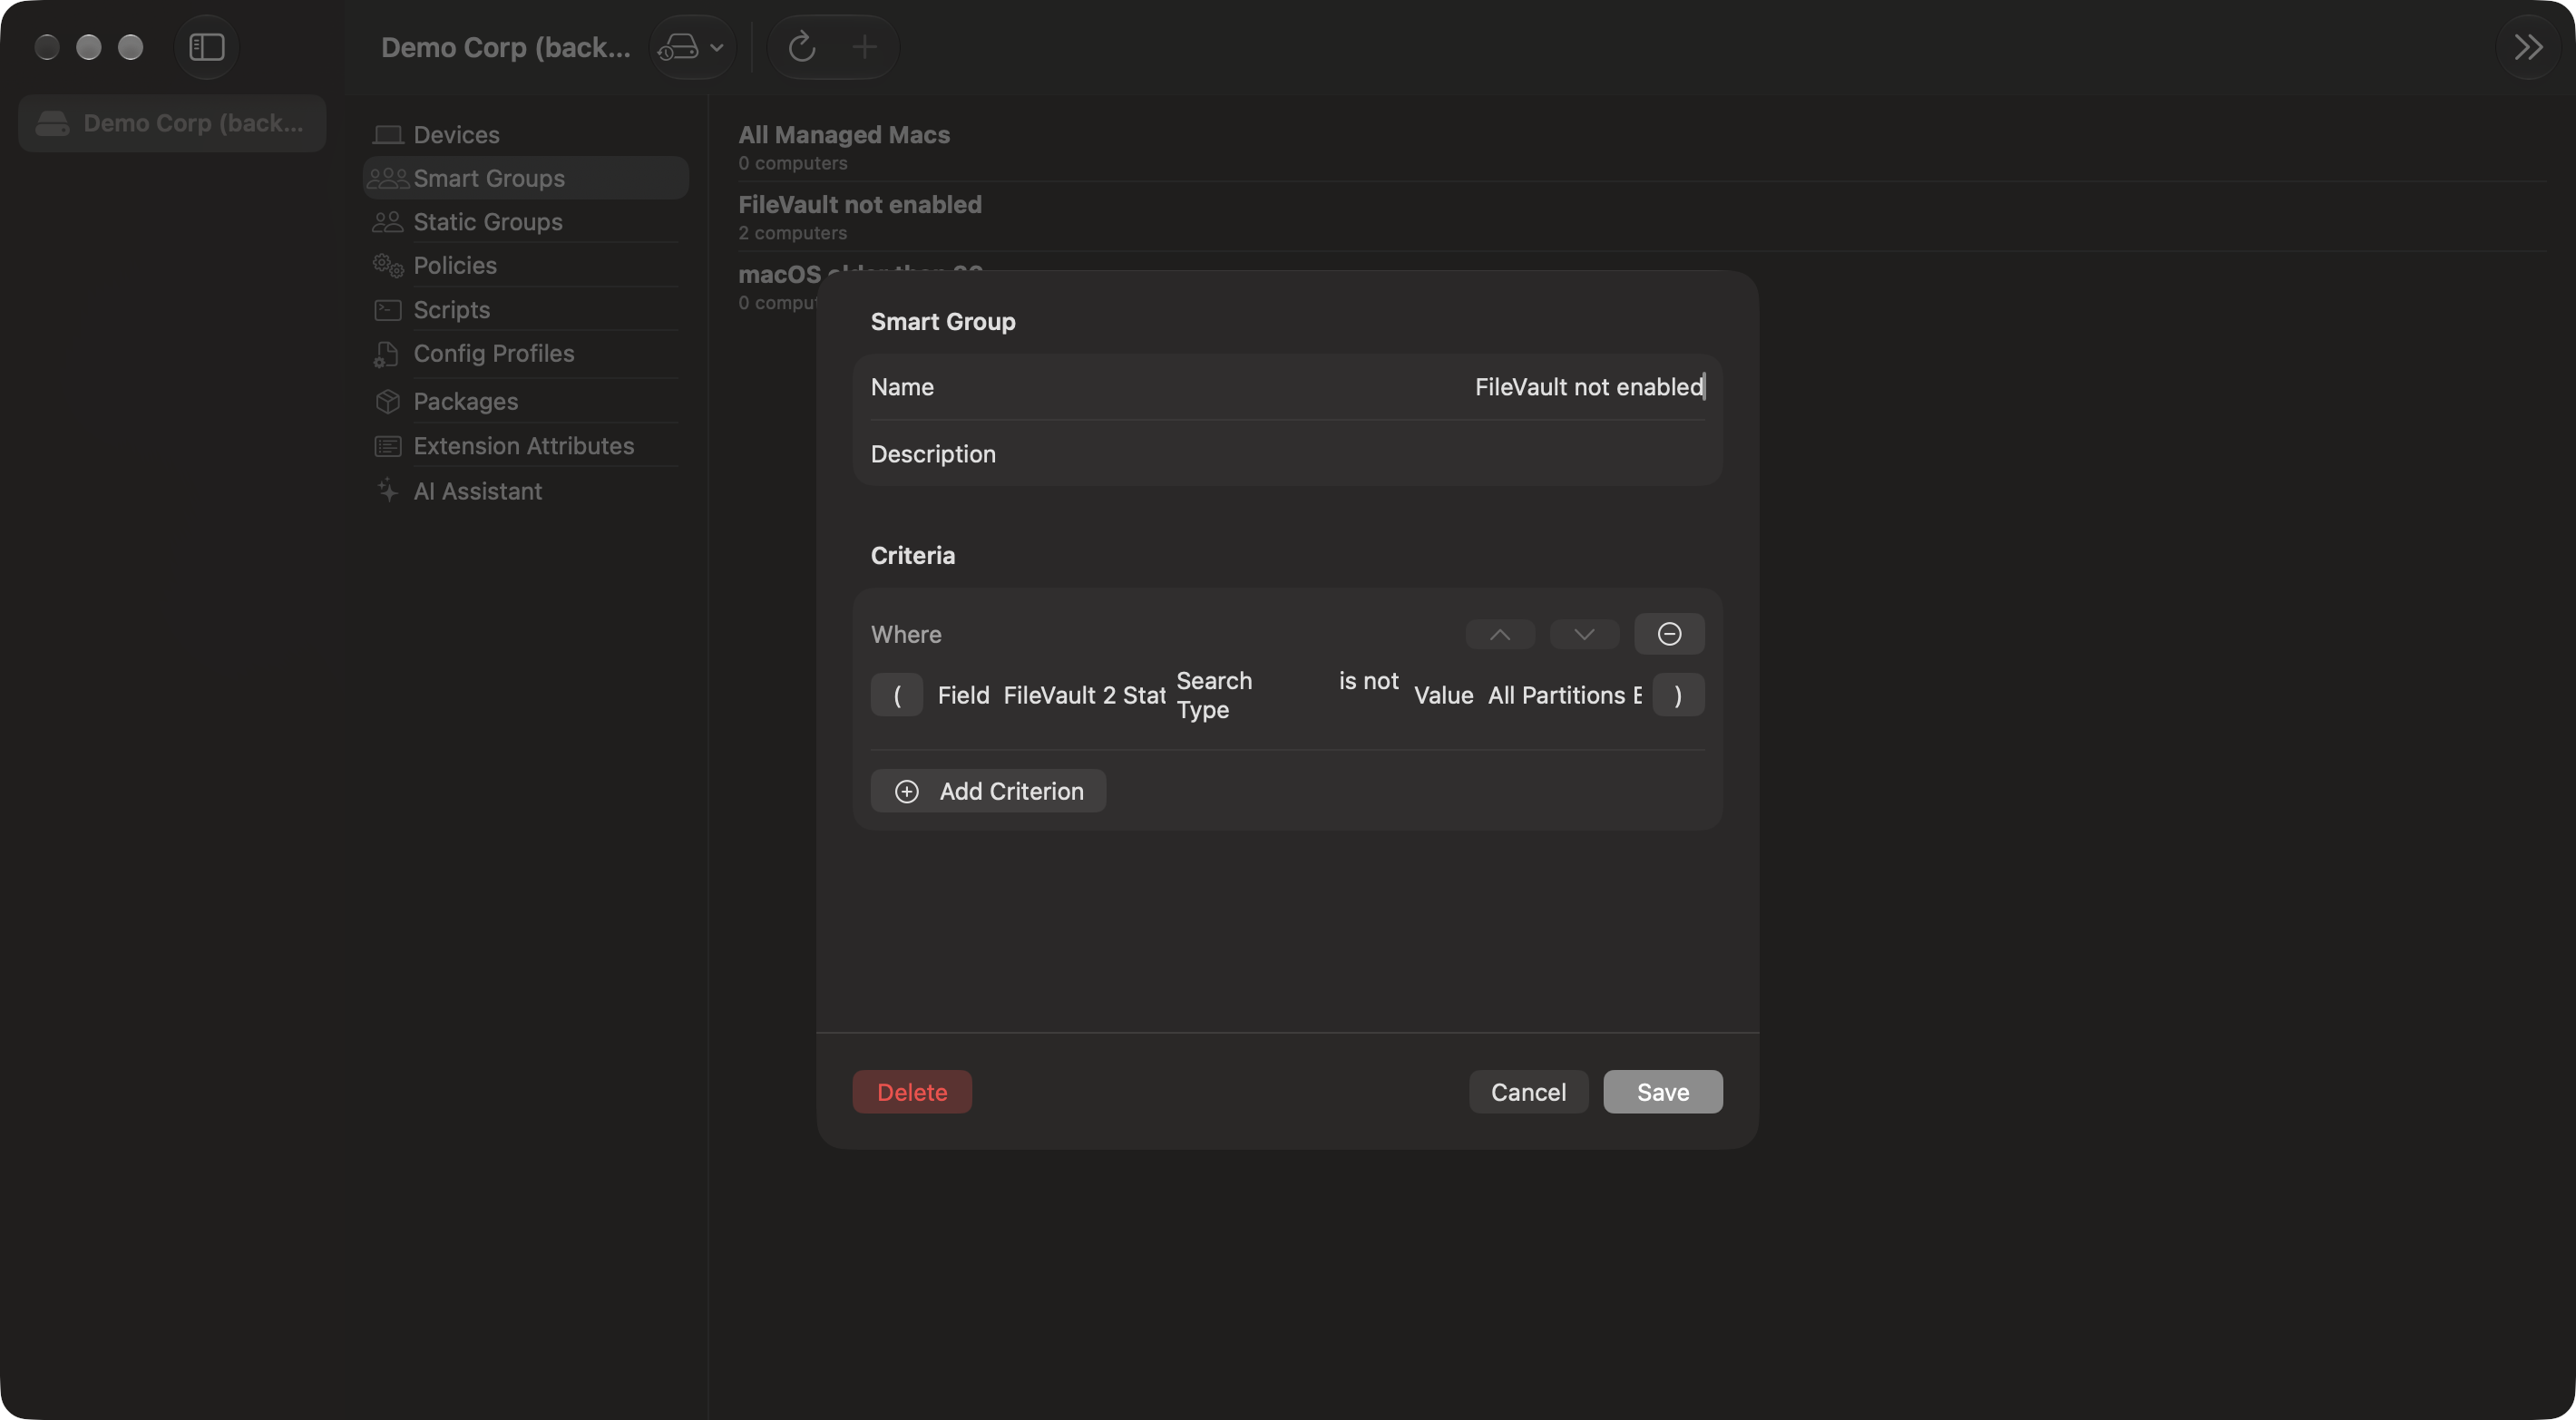
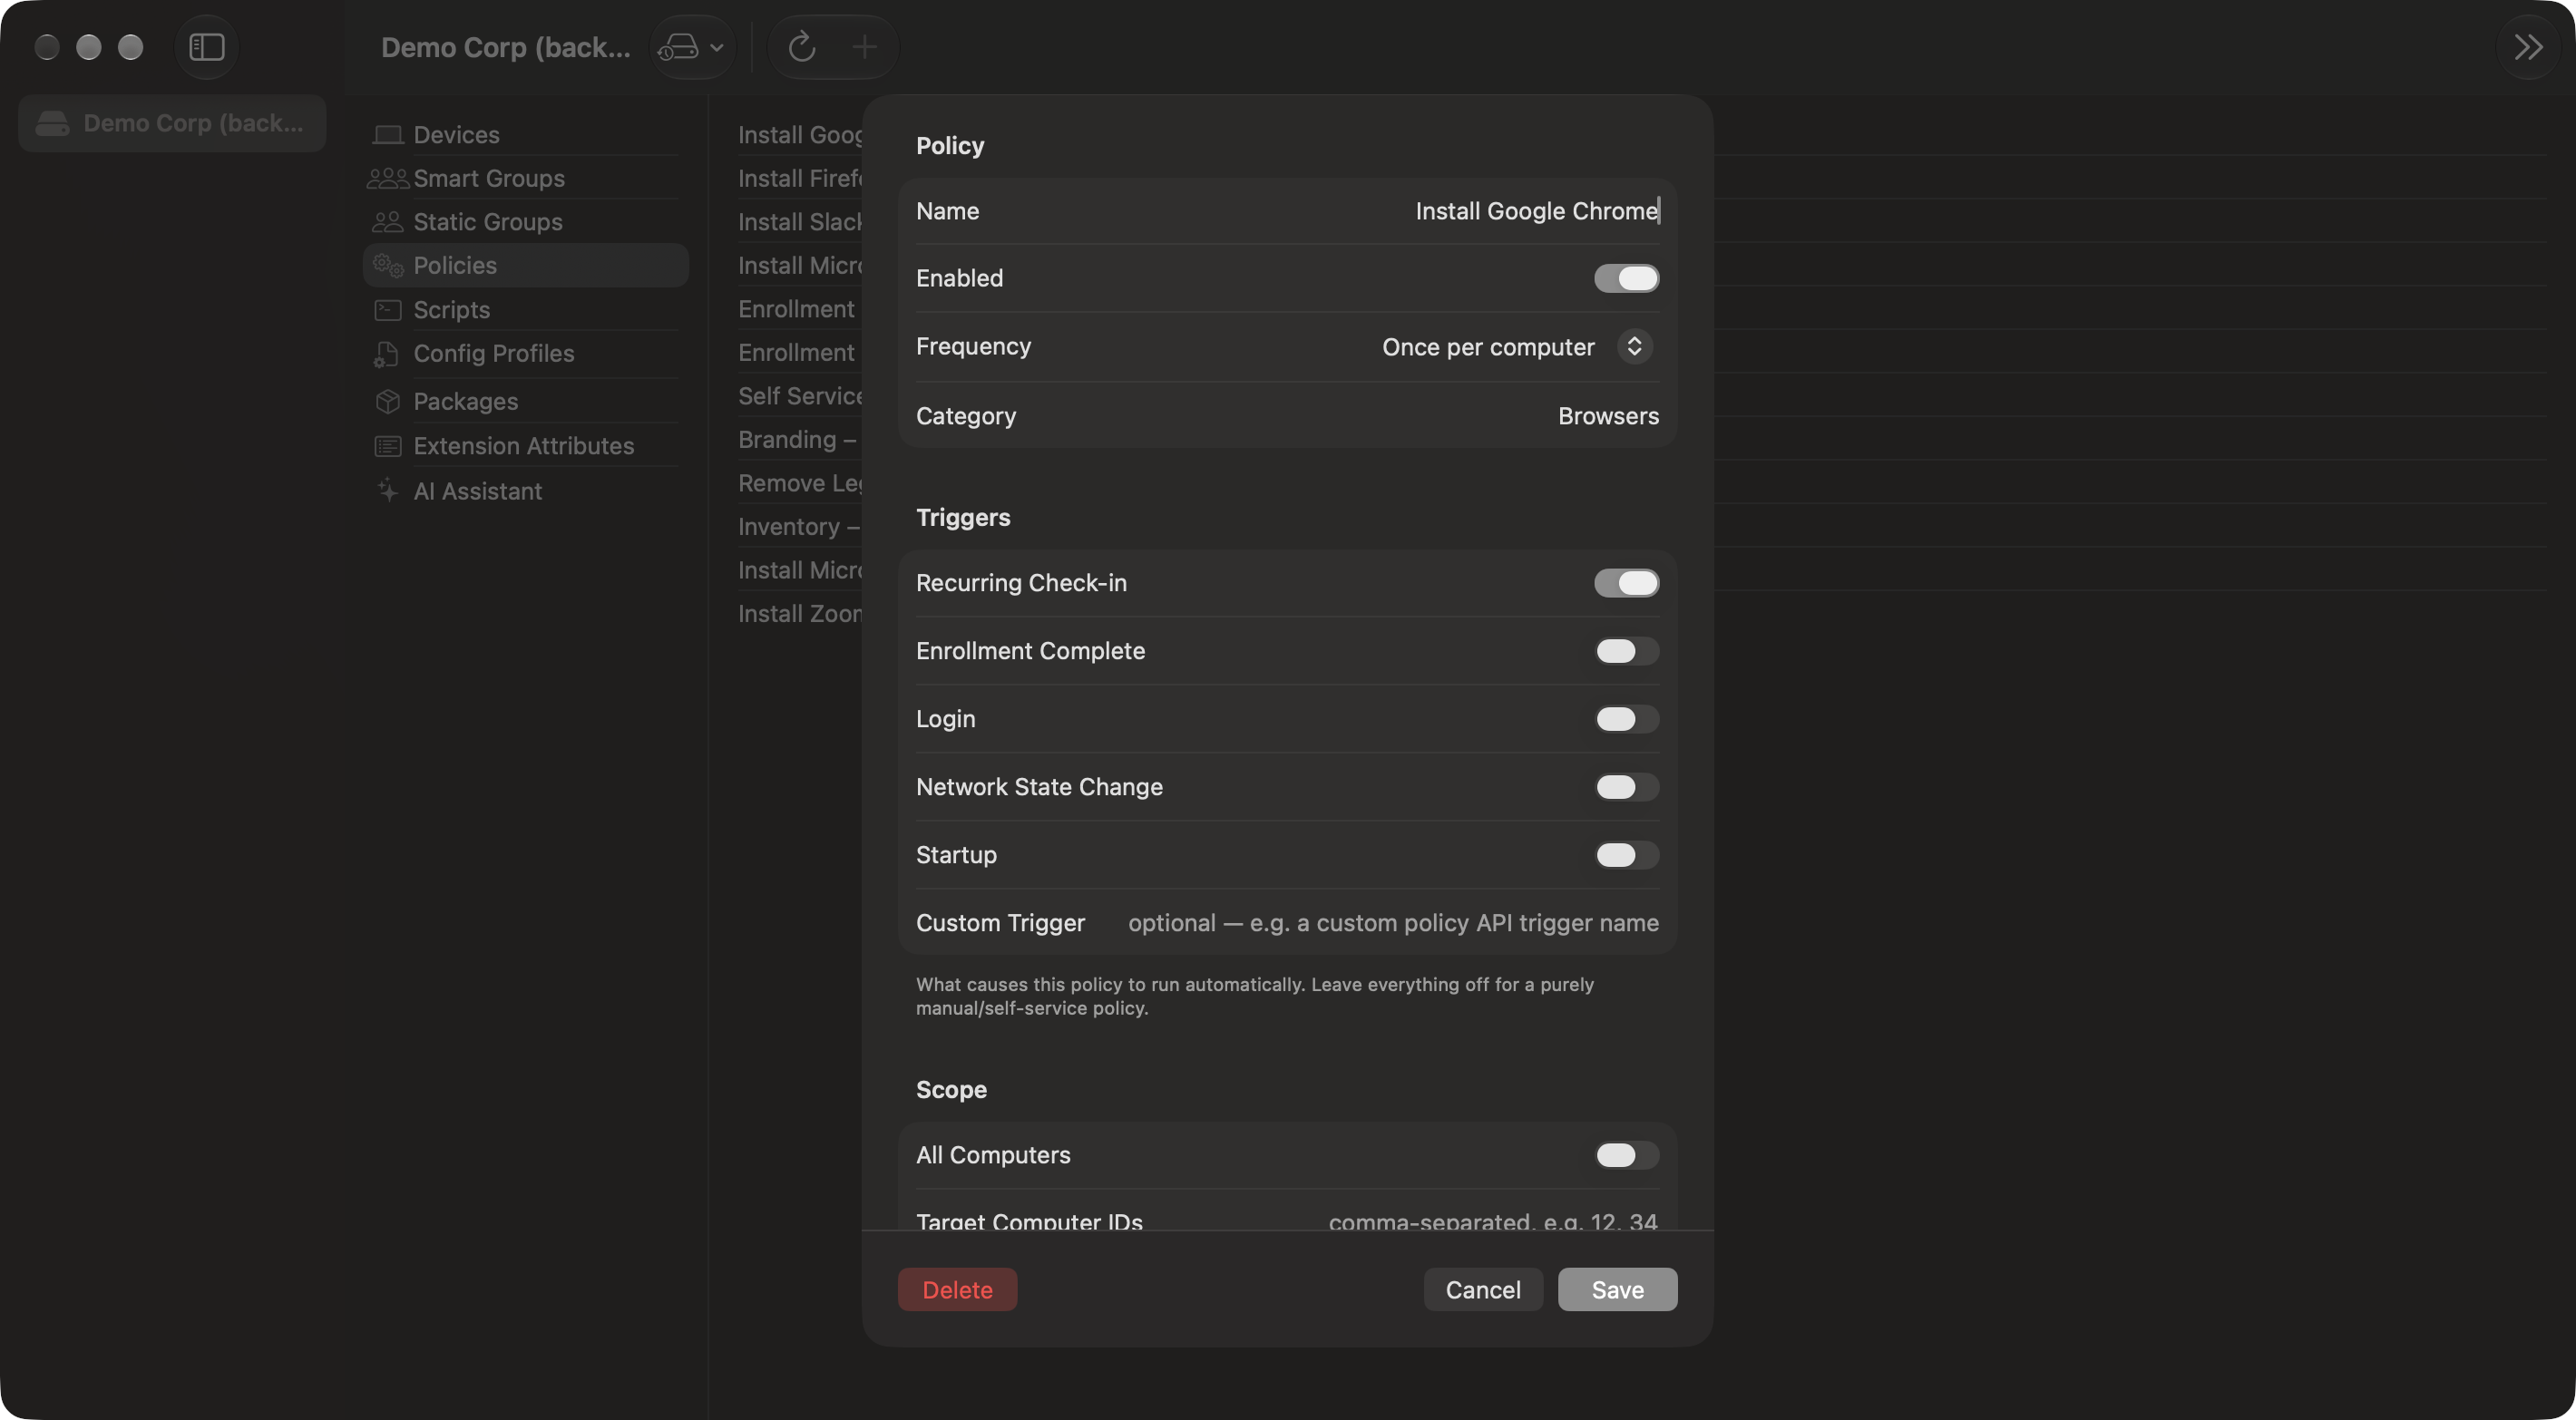
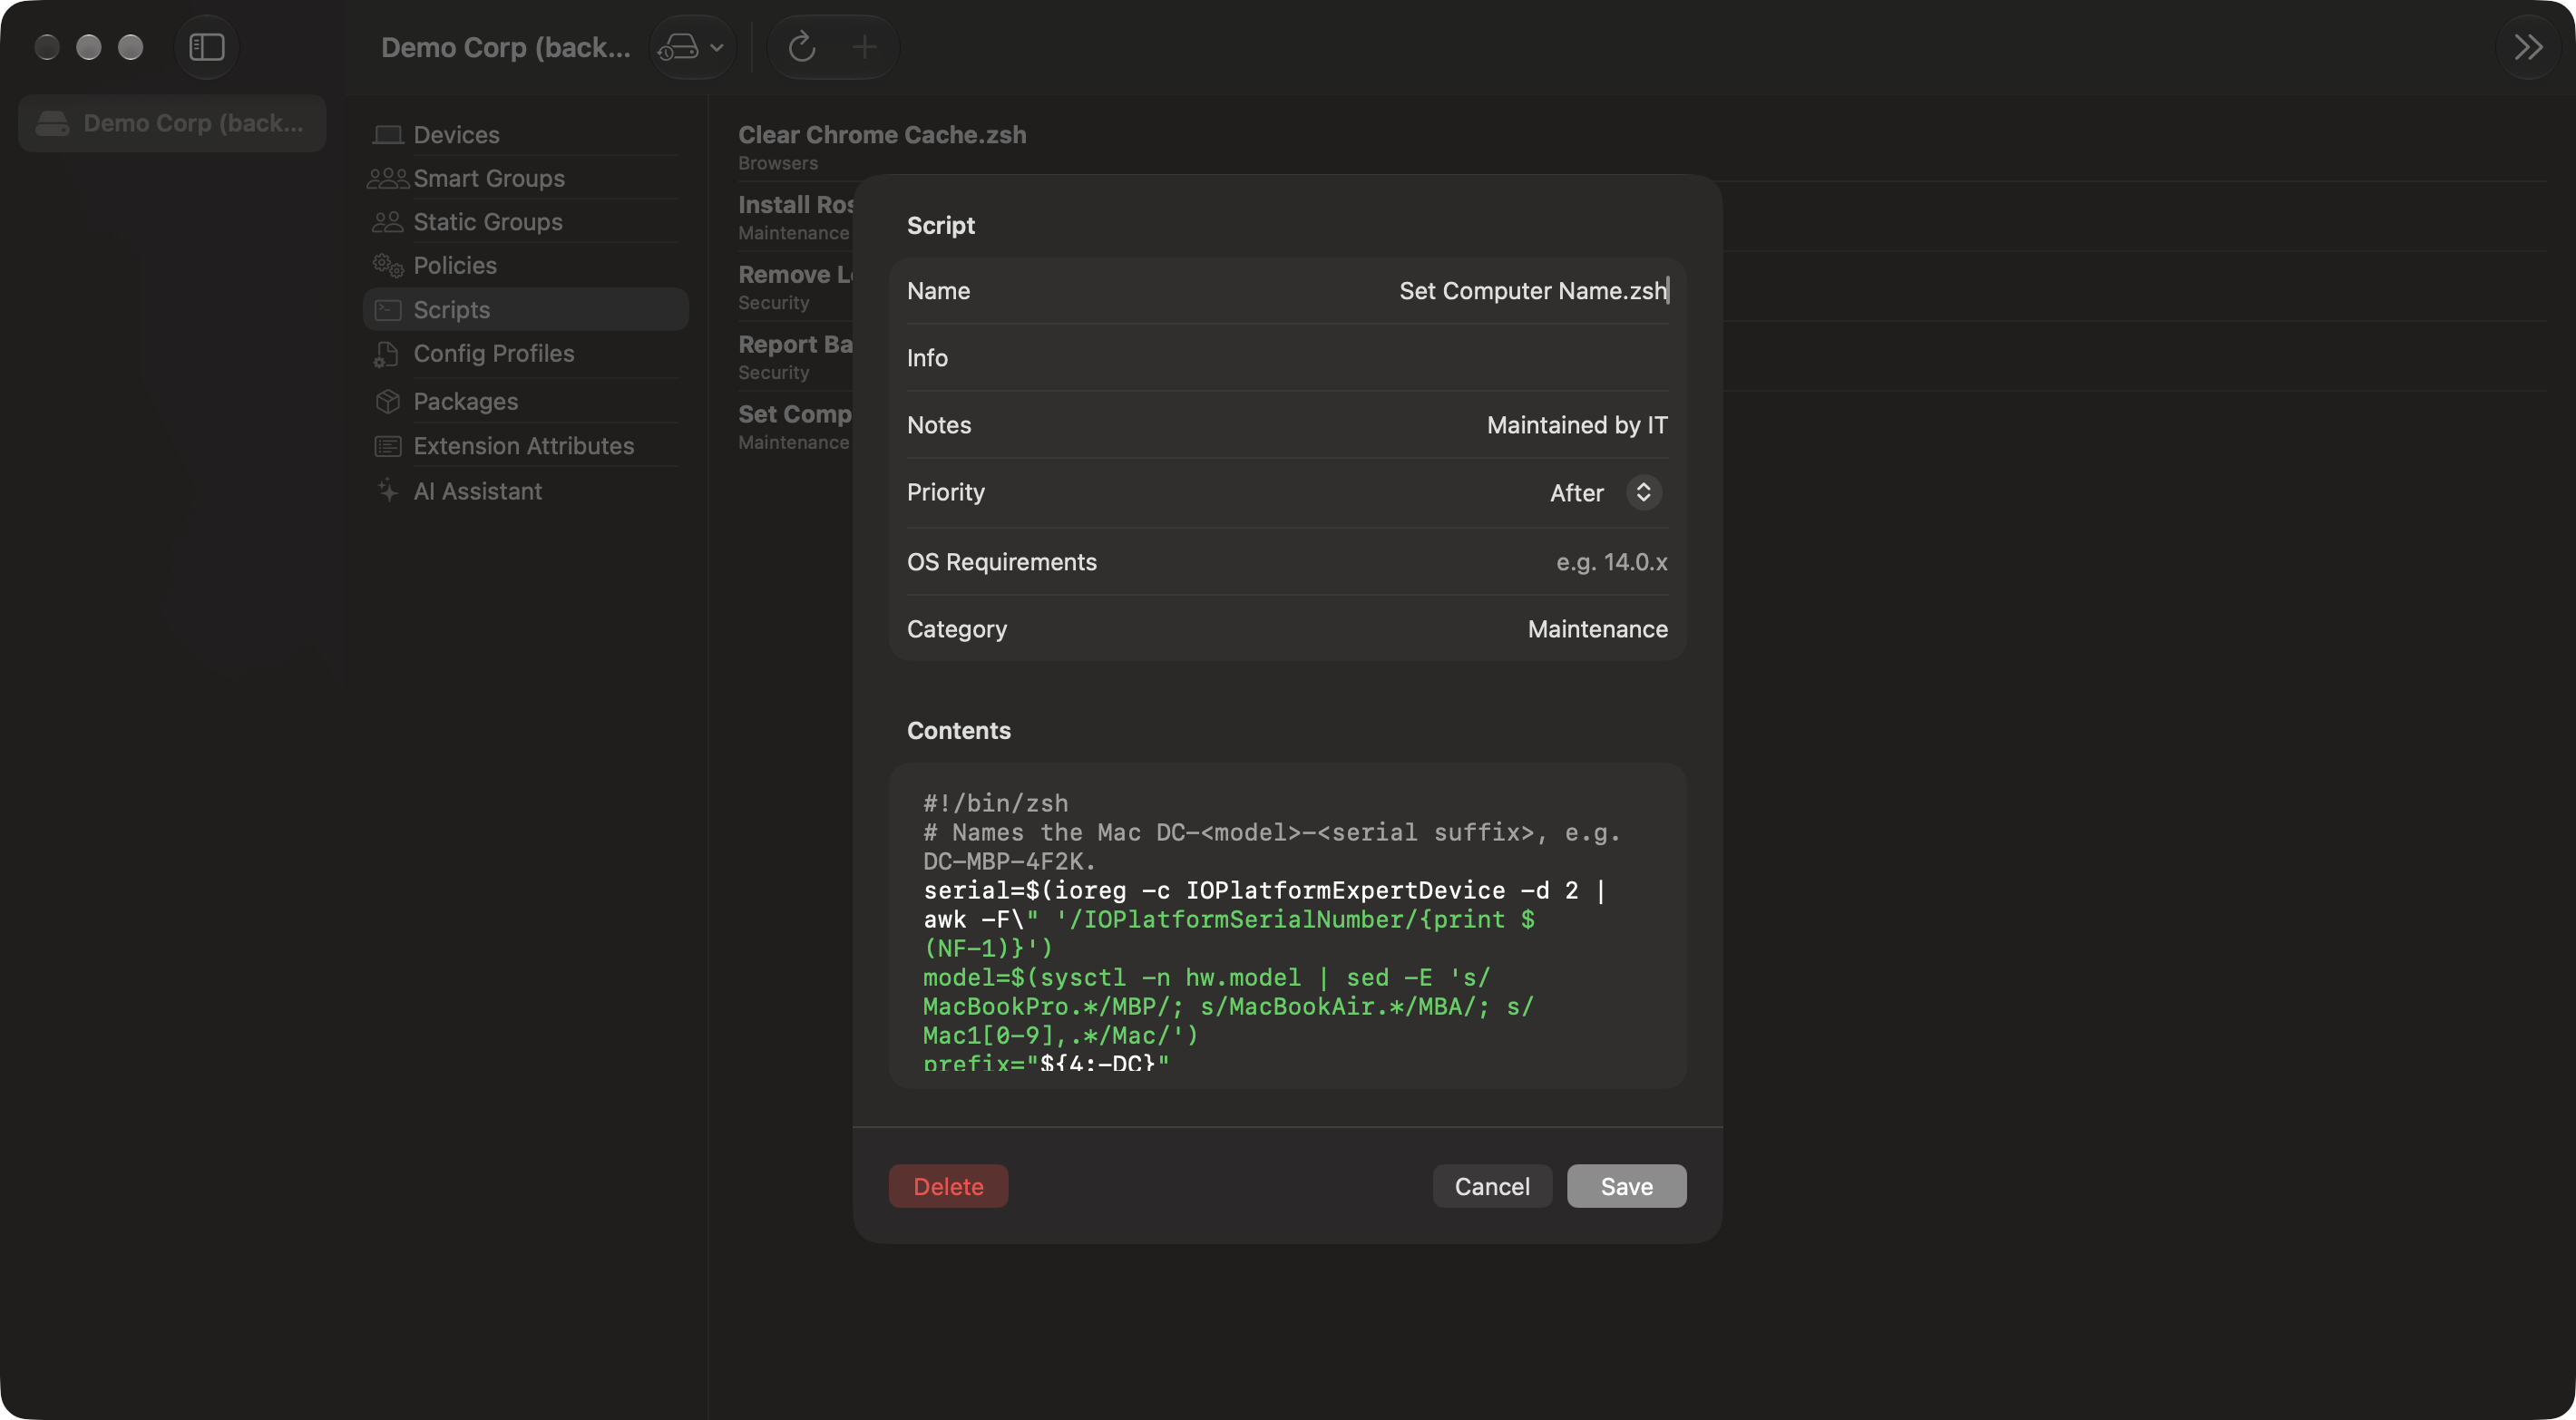
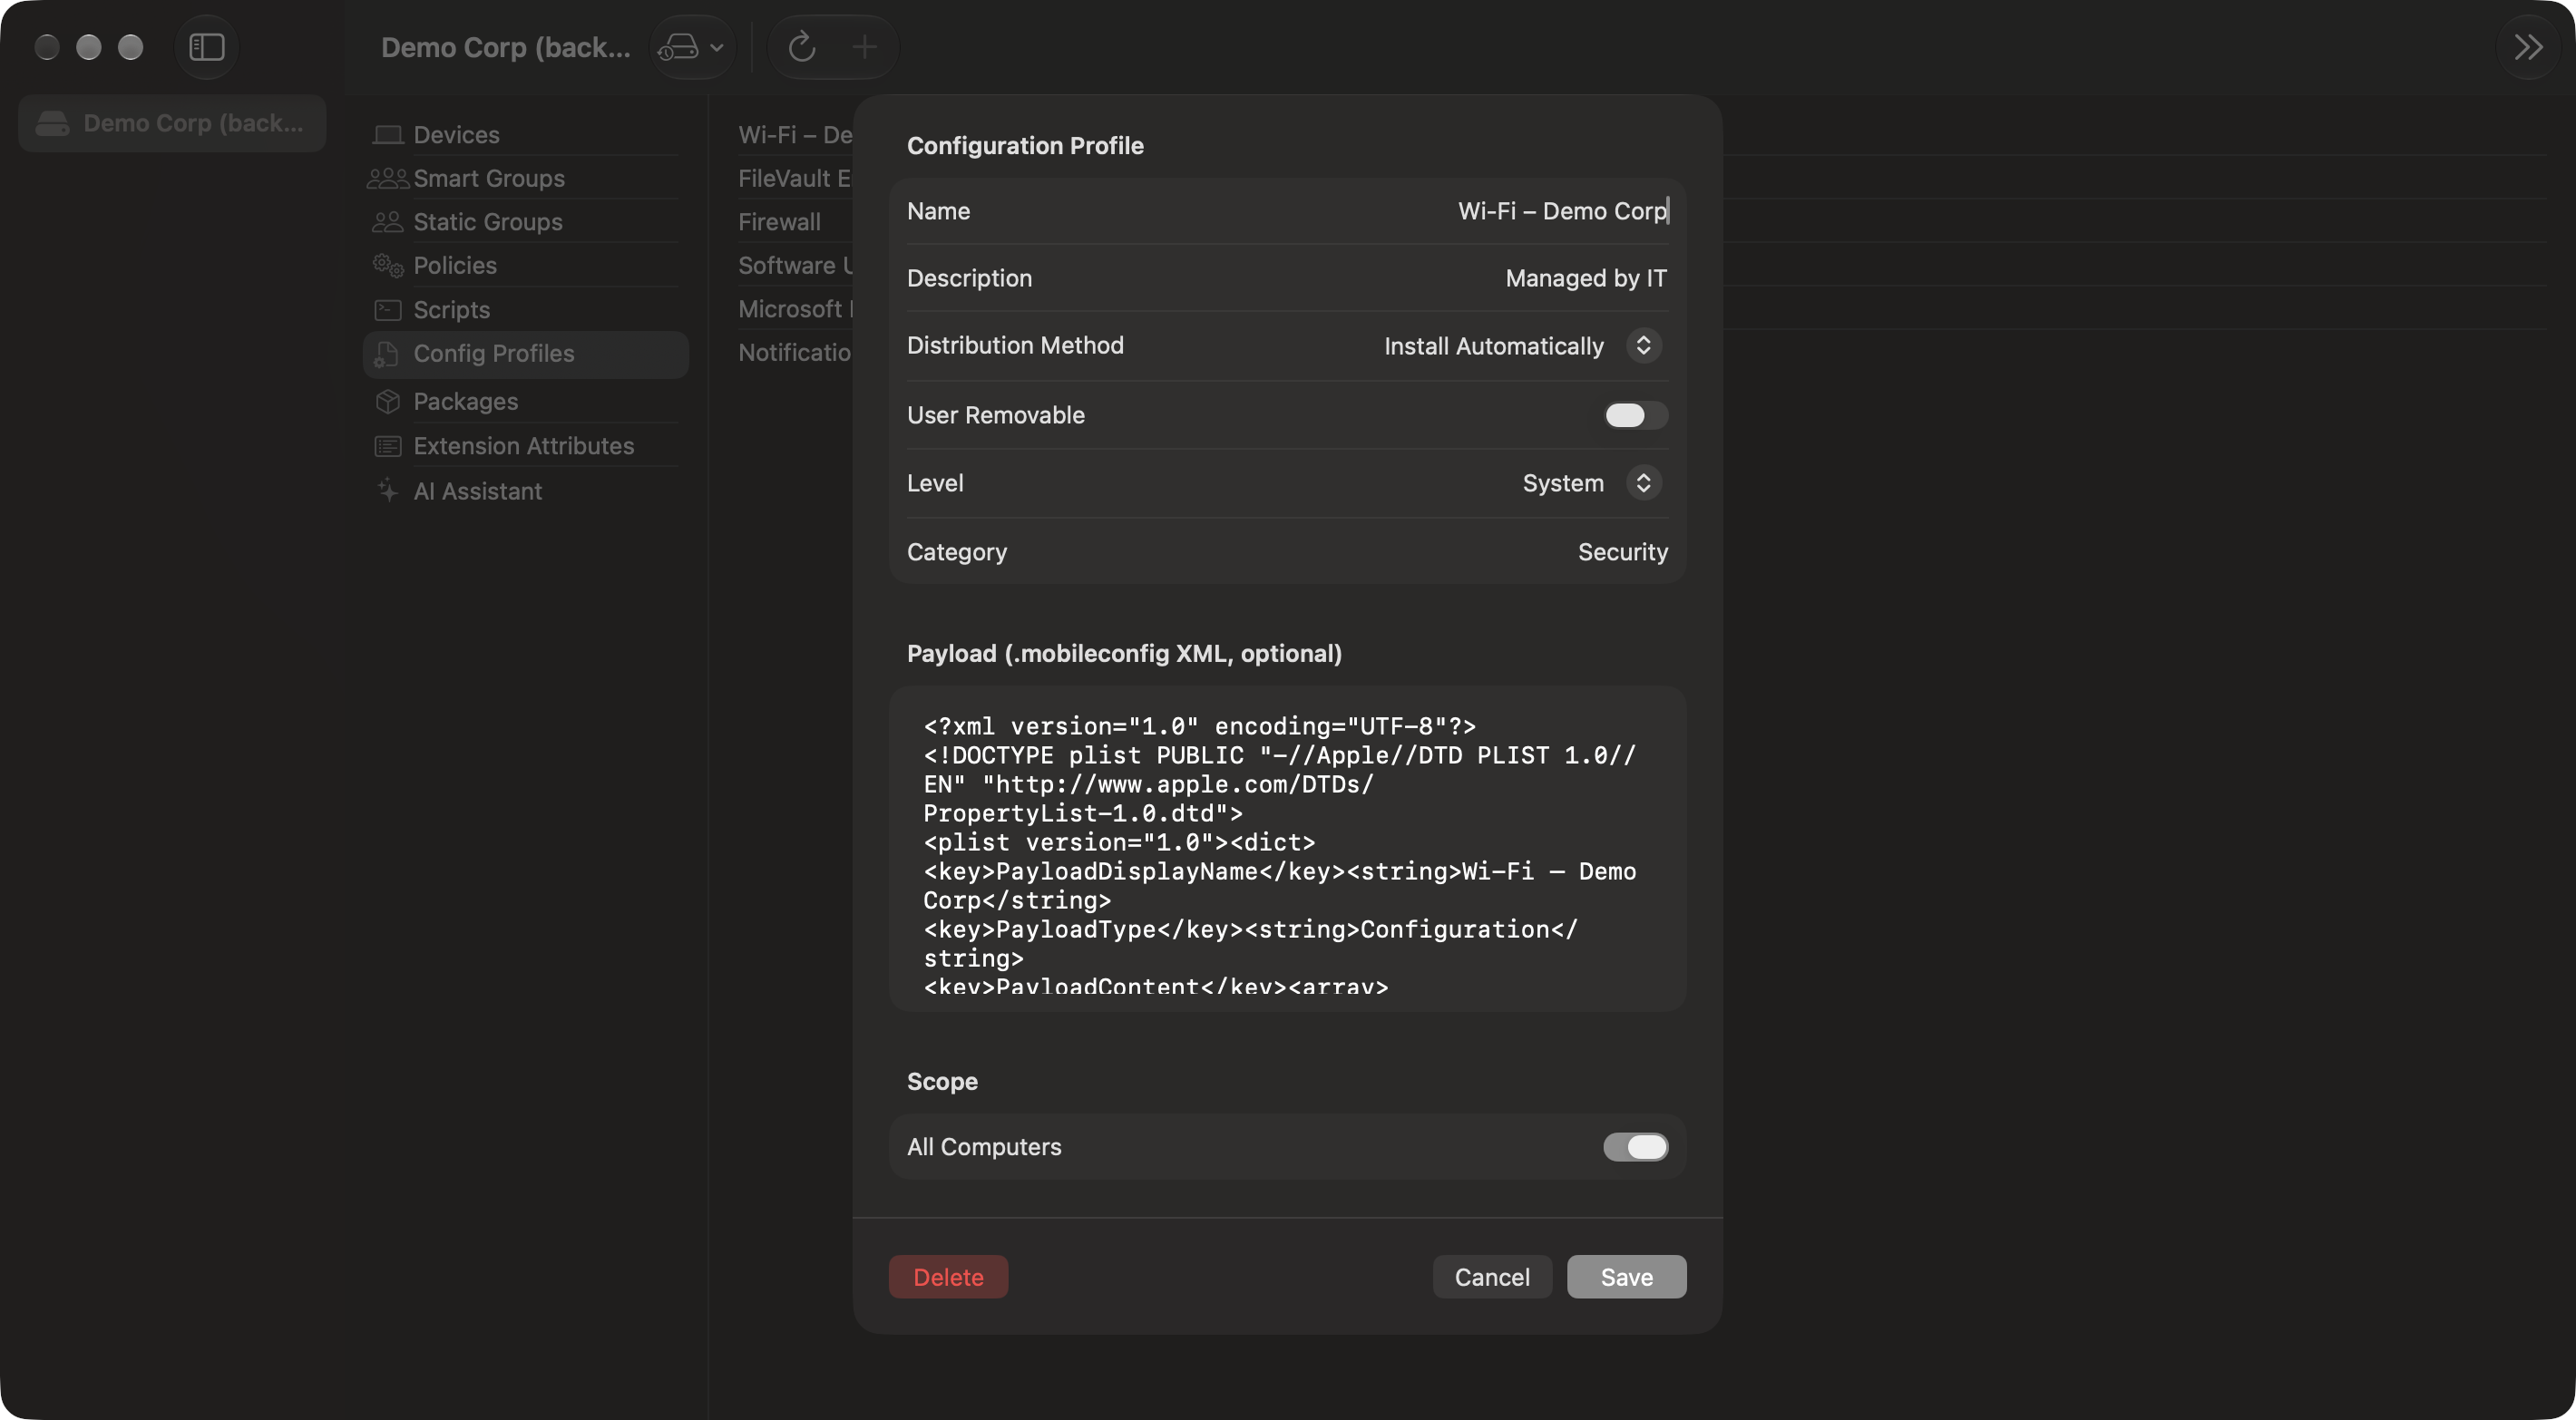
Full CRUD for Policies, Smart Groups, Scripts and Configuration Profiles, following Jamf's current API — not the deprecated Classic API.
🧭
Patch & Compliance
Reporting views for patch status and compliance across every org you manage, exportable as PDF or CSV.
🔎
Global Search
Search across every resource type at once — devices, groups, policies, profiles, scripts and more — no matter which org they live in.